cPanel
Plesk
Ubuntu
Windows
Debian
CentOS
Docker
Kubernetes
Linux

DDoS Protection in Argentina with PacketZero

PacketZero is our own mitigation system: it stops attacks in the network before they reach your server, your prefixes or your access network. It protects our infrastructure every day, and it can protect yours too.

XDP / eBPFL3 · L4 · L7Buenos Aires · Miami · DallasGRE tunnel or interconnection

Last 30 days · measured on 11/11/2026

What we stopped in one month

Figures from our own network, taken from the same systems that feed the PacketZero panel.

the largest attack380.9 Mpps peak
700.6Gbps
attacks stopped at the network edge
1,570
dropped by our filters168.3 billion packets
71.1TB
of clean traffic delivered
447.7TB
protected IPs
766

The network edge stops volumetric floods; PacketZero filters drop what is left and deliver only legitimate traffic.

A 442.7 Gbps attack, layer by layer

This is how an attack against a FiveM server protected by PacketZero was recorded. We removed the IP and the customer's name; the figures are as measured.

Attack report ·

Mitigated
Type
UDP flood
Target
FiveM server · port 30120/UDP
Sources
18,936 IPs from Brazil, Mexico, Malaysia, and Ukraine
Result
The server stayed online
  1. 01

    Network edge

    The bulk of the attack is stopped at the edge, before it enters our network.

    442.7Gbps

    43.5 Mpps peak

  2. 02

    PacketZero filters

    Our filters dropped what got past the edge using the FiveM profile: only traffic that behaves like a player goes through.

    20.3Gbps

    peak past the edge · 1.57 TB dropped

  3. 03

    Your server

    The server received its usual traffic and stayed online throughout the attack.

    37Mbps

    at most, its legitimate traffic

Bars to scale: the server received 0.008% of the attack's peak.

Four ways to use PacketZero

From a server in our datacenter to your own network. Servers have published prices; everything else is quoted to fit.

01At inetHost

Your server in our datacenter

VPS, bare metal or colocation in Buenos Aires with PacketZero in front. You order the server and the protection comes with it.

  • Cloud Mitigated: VPS with DDoS filters for games
  • Bare metal and colocation with PacketZero on your IPs
  • Rules panel included

02Your infrastructure

Your network, over GRE or interconnection

We announce your prefixes over BGP, filter the attacks and hand the clean traffic back over a GRE tunnel or a physical interconnection in our Buenos Aires datacenters.

  • From your own /24
  • No need to change your transit provider
  • Attacks spread across the whole range (carpet bombing)
  • For ISPs, hosting companies and game networks

03In your network

PacketZero inside your infrastructure

We deploy and operate PacketZero in your own network, in front of your servers, with the same profiles and rules we use in ours.

  • Deployment and operation handled by us
  • Game profiles and per-port rules
  • Panel to see attacks and build rules
  • Can be combined with filtering in our network for attacks larger than your links

04Self-service

Own panel and API

At packetzero.inethost.com.ar you see your attacks, your traffic and your rules, and change them yourself without opening a ticket.

  • Per-port rules, whitelist, blacklist and country blocking
  • Attack alerts on Discord and Telegram
  • API and Pterodactyl / TCAdmin integration

Connectivity with mitigation built in

Besides protecting what you already have, we provide the connection itself with PacketZero in front.

See all connectivity →

For ISPs and hosting

Mitigated IP transit

BGP transit with PacketZero in front: attacks are stopped before they reach your network and you receive only clean traffic.

  • BGP session with full table or default route
  • At any of our points of presence
  • Protection for all your prefixes, including carpet bombing

How we hand back your clean traffic

When we protect your prefixes, you choose how the filtered traffic reaches you. Both options use BGP and the same filter.

GRE tunnel

Where you are
Any datacenter or network with a public IP
How it connects
GRE tunnel over the internet to your router
Routing
We announce your prefixes over BGP and deliver them through the tunnel
Keep in mind
The tunnel adds a header: MTU and MSS need adjusting
Best for
Hosting and game networks anywhere

Physical interconnection

Where you are
At any of our points of presence: CABASE, Cirion, Telecom, PIT Argentina, PIT Chile, IX.br SP4 or Colohouse Miami
How it connects
Cross-connect or fiber, at L2 (VLAN) or L3
Routing
Direct BGP session with your router
Keep in mind
You need a physical presence at our datacenter
Best for
ISPs and high-traffic networks in Buenos Aires

What you need

  • Your own ASN

    A registered autonomous system for the BGP sessions.

  • Prefixes from /24

    The smallest prefix accepted over BGP on the internet.

  • A BGP router

    MikroTik, Juniper, Cisco or Linux with FRR.

  • A technical contact

    Someone on your team to coordinate rollout and testing.

The PacketZero panel

What our customers see: every attack, the traffic and the rules of each IP. Screenshots from a test account (panel in Spanish), with IPs blurred.

packetzero.inethost.com.ar ↗
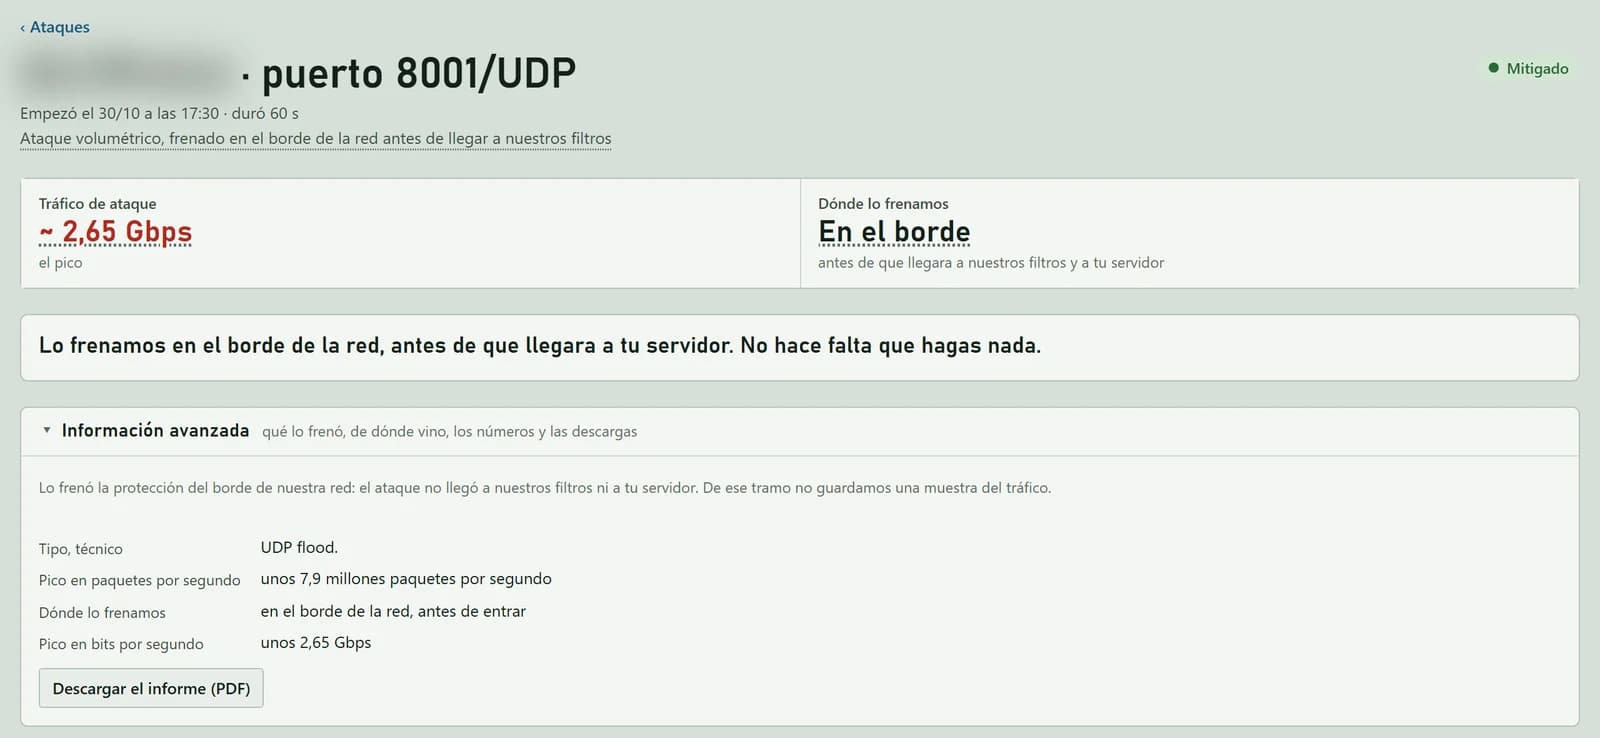
01Every attack, explainedWhen it started, how long it lasted, the peak and where we stopped it, with a downloadable PDF report.
PacketZero panel: detail of a 2.65 Gbps UDP attack stopped at the network edge, with technical information and a button to download the PDF report
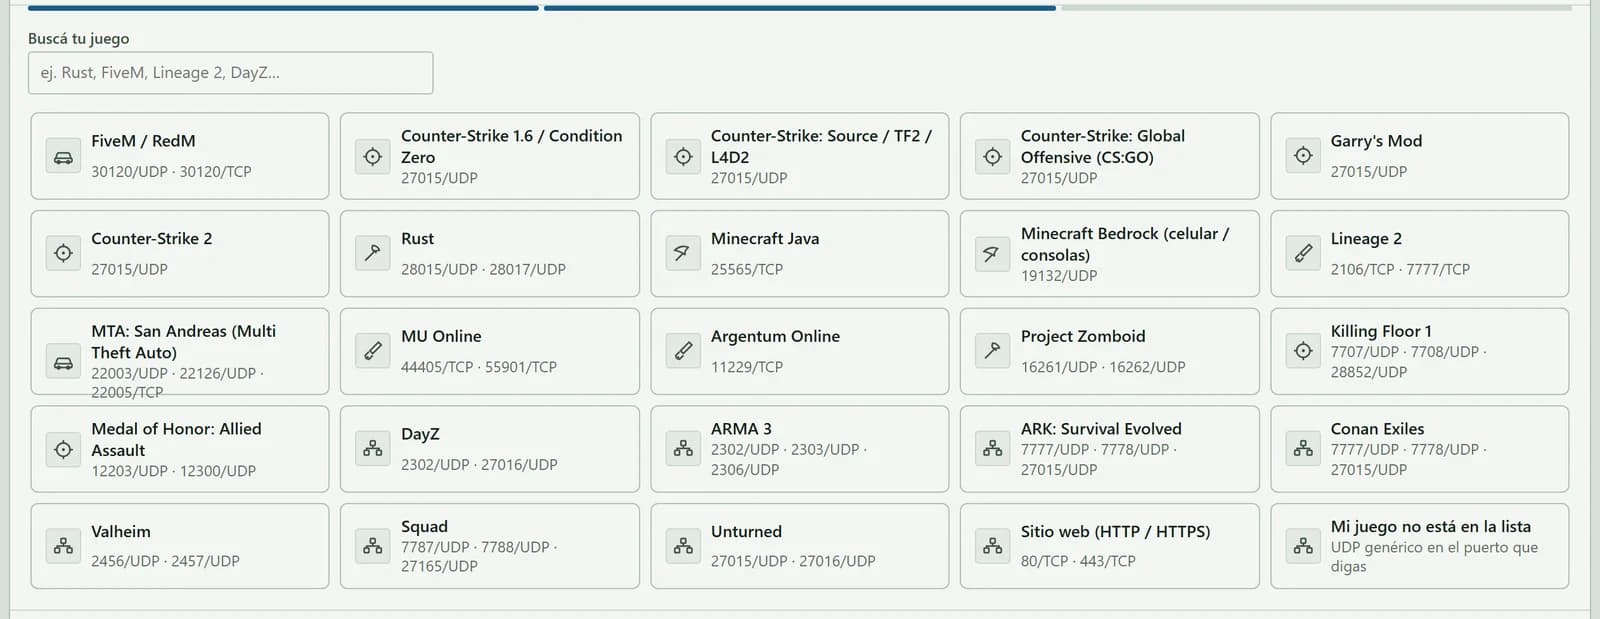
02Game profilesPick your game and the filter already knows which ports and traffic to expect.
PacketZero panel: game profile picker with FiveM, Counter-Strike 2, Rust, Minecraft, MTA: San Andreas, Lineage 2 and others, each with its ports
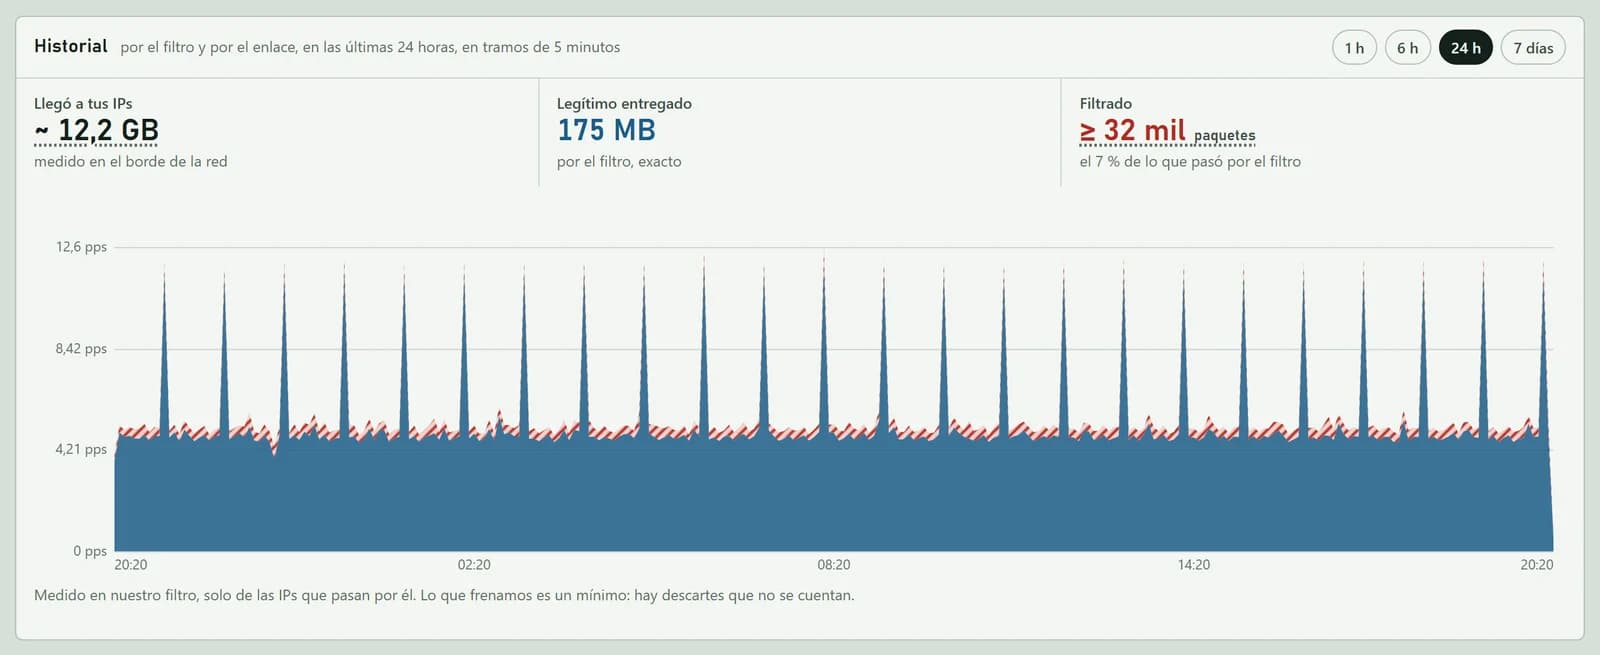
03Traffic and historyWhat reached your IPs, the legitimate traffic delivered and what was filtered, in 5-minute slots.
PacketZero panel: 24-hour traffic history showing traffic that reached the IPs, legitimate traffic delivered and filtered traffic
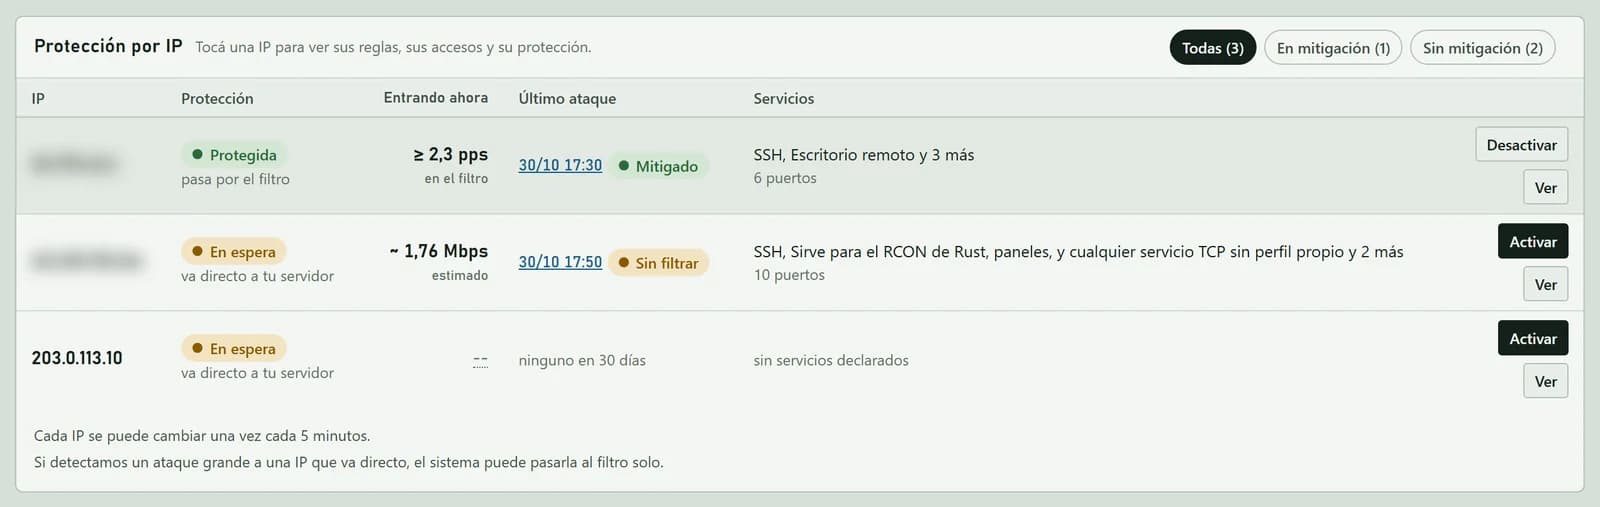
04Per-IP protectionTurn the filter on per IP and see its declared services and its last attack.
PacketZero panel: per-IP protection table with filter status, incoming traffic, last attack and services of each IP

What PacketZero does

Our own filtering, built for games and real-time services, run by our network team in Buenos Aires.

  • XDP/eBPF filtering

    Attack packets are dropped as soon as they reach the network card, before going through the rest of the system.

  • Layers 3, 4 and 7

    From volumetric floods to attacks that mimic your game's or your website's protocol.

  • Game profiles

    Each profile knows what traffic to expect on each port, so the attack is cut and players keep joining.

  • Rules, lists and countries

    Per-port rules, whitelist, blacklist and country blocking, per IP.

  • Discord and Telegram alerts

    We let you know when an attack against your IPs starts.

  • API and integrations

    Our own API plus Pterodactyl and TCAdmin integration, so rules follow your servers.

Some profiles

  • FiveM / RedM
  • Counter-Strike 2
  • CS 1.6
  • Rust
  • Minecraft
  • MTA / SA-MP
  • Garry's Mod
  • Lineage 2
  • MU Online
  • Argentum Online
  • Project Zomboid
  • DayZ
  • ARK
  • Valheim

Where we filter

Filtering nodes in four locations, plus scrubbing at the network edge for volumetric attacks.

  • Buenos AiresOwn datacenter
  • Buenos AiresCirion
  • MiamiUnited States
  • DallasUnited States

Network edge: upstream scrubbing of volumetric floods

Points of presence

We are present at these exchange points and datacenters: you can interconnect with us there and receive mitigated traffic.

  • PIT ChileSantiago, Chile
  • CABASEBuenos Aires
  • CirionBuenos Aires
  • TelecomBuenos Aires
  • PIT ArgentinaArgentina
  • IX.br SP4São Paulo, Brazil
  • ColohouseMiami, United States

Frequently asked questions

What people ask us most about DDoS mitigation.

Request a quote

Preparing the form…

DDoS Protection and Mitigated Internet in Argentina | inetHost